Blog
Test Plan vs Test Strategy: Key Differences, Scope, and When to Use Each

Andy Dickin
Published on

Table of contents
Lorem ipsum
Lorem ipsum
Lorem ipsum
Lorem ipsum
Lorem ipsum
Most teams know they need both a test strategy and a test plan. Fewer teams are clear on what each document actually does, who it is for, and why conflating the two creates problems that show up weeks later when a project is already in motion.
The confusion is understandable. Both documents are about testing. Both involve thinking through what needs to be validated and how. But they operate at fundamentally different levels, serve different audiences, and answer different questions. Getting this wrong has real consequences:
A test strategy written at project level gets rewritten for every new project, creating inconsistency across teams and wasted effort
A test plan written at organisational level is too abstract to guide day-to-day testing and gets ignored by the people who should be using it
Teams without a strategy make the same tool and methodology decisions repeatedly, accumulating technical debt in the testing programme
Teams without a plan have strategic intent but no execution framework, and quality outcomes become unpredictable
This guide clarifies what each document is, what it contains, when to create it, and how the two work together to create a testing programme that is both consistent and actionable.
Understanding Test Strategy
A software test strategy is a high-level document that defines the overall approach to testing across an organisation or programme. Unlike a test plan, which is tied to a specific project or release, a test strategy sits above individual projects and provides the consistent framework that all testing activity should align with.
Think of it as the constitution of your testing programme. It does not tell testers what to do on a given Tuesday. It establishes the principles, standards, and boundaries within which all testing decisions are made.
A well-written test strategy answers questions that should not have to be re-answered for every project:
What types of testing does the organisation consider mandatory?
What is the standard approach to automation?
How does the organisation assess and prioritise testing risk?
What tools are approved and on what basis were they selected?
How is testing quality measured and by whom?
Test Strategy Scope
A test strategy operates at the organisational or programme level, not the project level. It provides guidance applicable across multiple projects over extended timeframes, typically six to twenty-four months.
This breadth is intentional. A strategy that needs rewriting for every project is not a strategy. It is a plan with extra steps. The scope of a test strategy typically covers:
All testing activity across a product portfolio or programme
Multiple teams who need consistent standards and approaches
Both current delivery priorities and future planning horizons
Strategy Components
A complete test strategy addresses every dimension of how testing is conducted, not just what types of testing exist. Each component serves a specific purpose in creating a coherent and governable testing programme.
Testing philosophy and quality objectives: The foundational beliefs about what quality means for the organisation and what testing is designed to achieve
Testing types and coverage targets: Which types of testing are required, when they apply, and what level of coverage is expected for each
Automation strategy and tool selection: What should be automated, what criteria tools must meet, and how the automation programme is governed
Resource allocation and team structure: How testing capacity is organised, what skills are required, and how resources are distributed across projects
Risk management approach: How testing risk is identified, classified, and prioritised so that effort goes where it matters most
Metrics and success criteria: How testing effectiveness is measured and what outcomes constitute a successful testing programme
Standards and best practices: The organisational norms that all testing activity should follow regardless of the project or team involved
Who Creates Test Strategy
A test strategy is not a document that gets written by whoever has spare capacity. It reflects strategic decisions about quality that require authority, experience, and a cross-functional perspective.
Test strategies are typically created and owned by:
QA leadership and test architects who understand both the technical testing landscape and the organisational context
Senior management who can connect testing objectives to business goals and secure the resources the strategy requires
Key stakeholders from development, product, and operations who need to be aligned on the quality standards the strategy establishes
Because the strategy is a long-lived document, ownership and review responsibility must be explicitly assigned. A strategy without a named owner tends to become outdated without anyone noticing.
Strategy Purpose
The primary purpose of a test strategy is consistency. Without it, each project team makes its own decisions about how to test, what tools to use, and what quality standards to apply. The result is an organisation where testing quality varies project by project, tool sprawl creates integration overhead, and there is no shared language for discussing testing risk or coverage.
A test strategy ensures that:
Testing approaches are consistent across projects and teams, making quality outcomes comparable and improvable over time
New projects can begin with a proven framework rather than designing their approach from scratch
Testing investment decisions are made strategically rather than reactively
Quality standards are documented and can be demonstrated to stakeholders, auditors, or regulators when required
Types of Test Strategies
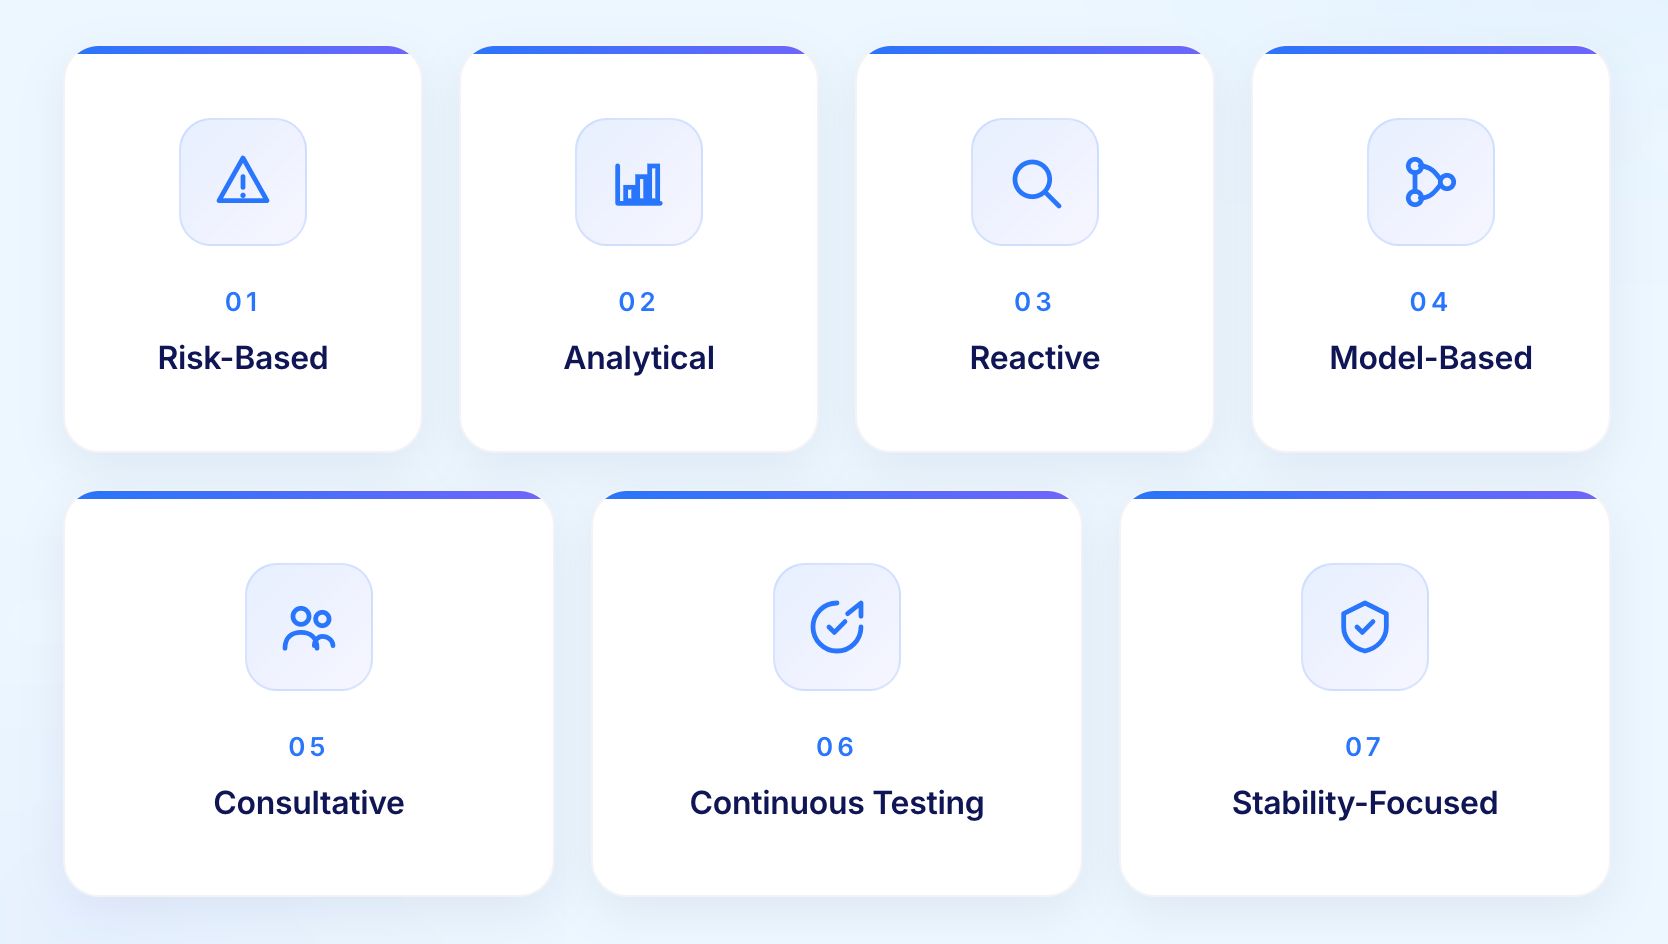
Not every project or organisation requires the same testing approach. Understanding which type fits your context prevents teams from applying a generic framework where a targeted one would be more effective.
Risk-Based Strategy
Testing effort is allocated proportionally to risk
High-impact, high-probability failure areas receive the deepest coverage
Lower-risk areas receive lighter validation
Best suited to teams with limited time who need deliberate prioritisation decisions
Analytical Strategy
Test cases are derived from systematic analysis of requirements or specifications
Every test traces back to a documented requirement
Well-suited to regulated industries where traceability is a compliance requirement
Requirements-based and model-based testing fall under this category
Reactive Strategy
Testing responds to what is discovered during execution rather than following a predetermined script
Exploratory testing is the most common form
Works well in dynamic environments where requirements are incomplete or evolving
Human judgement and curiosity are the primary defect-finding tools
Model-Based Strategy
Tests are generated from formal models of expected application behaviour
State machines, decision tables, and flow diagrams serve as the source of truth
Suits applications with well-defined, complex business logic
Best applied where the cost of missed defects is high
Consultative Strategy
Testing priorities are shaped by input from subject matter experts, stakeholders, or end users
Incorporates domain knowledge that may not be captured in formal requirements
Useful when technical specifications alone do not reflect real usage patterns
Continuous Testing Strategy
Automated tests run continuously throughout the delivery pipeline
Provides feedback at every stage from development through deployment
Underpins DevOps and CI/CD delivery models
Every code change is validated automatically before progressing
Stability-Focused Strategy
Regression testing is the primary activity
Goal is ensuring that changes do not break existing functionality
Common in mature products with large existing user bases
Stability takes priority over new feature velocity

Understanding Test Plan
A test plan is a detailed, project-specific document that specifies exactly what will be tested, how it will be tested, who will test it, and when. Where the test strategy establishes the organisational framework, the test plan translates that framework into concrete, actionable steps for a specific release, sprint, or implementation.
If the test strategy is the constitution, the test plan is the legislation. It takes the principles established at the strategic level and turns them into the specific decisions and assignments that guide a real testing programme from day one of execution through to sign-off.
A well-written test plan answers the questions that the test strategy deliberately leaves open:
Which specific features and user journeys are being tested in this release?
Who is responsible for each area of testing?
What does the testing schedule look like and what are the key milestones?
What conditions must be met before testing begins and before it is considered complete?
What risks are specific to this project and how will they be managed?
Test Plan Scope
A test plan is scoped to a single project, release, sprint, or implementation. Its lifespan is tied to the delivery it was created for, typically ranging from two weeks for a sprint plan to six months for a large implementation.
Unlike the test strategy which remains stable across projects, the test plan is a living document that evolves as the project evolves:
It is updated when requirements change
It is revised when resources or timelines shift
It is reviewed and signed off before testing begins
It is retired or archived when the release is complete
Plan Components
A complete test plan contains enough detail for any team member to understand what is being tested and why, without needing to ask. Each component addresses a specific dimension of execution planning.
Specific features and requirements under test: The precise scope of what is being validated in this release, with explicit statements about what is out of scope
Detailed test scenarios and cases: The specific workflows, conditions, and scenarios that testers will execute, linked to requirements where traceability is required
Test environment specifications: The hardware, software, network configurations, and tools required to execute the plan, including who is responsible for setup
Execution schedule and resource assignments: Who is testing what, in what order, and by when, with milestones that allow progress to be tracked
Entry and exit criteria: The conditions that must be met before testing starts and the conditions that must be met before testing is considered done
Deliverables and reports: The specific outputs the testing programme is expected to produce, including test results, defect reports, and sign-off documentation
Risks and contingencies: The project-specific risks that could affect testing and the specific contingency for each one
Who Creates Test Plan
A test plan is created by the people closest to the project being tested. It requires detailed knowledge of the specific requirements, the team, the environment, and the timeline.
Test plans are typically created by:
QA managers and test leads who have the authority to make resourcing and scheduling decisions and the experience to identify what needs to be covered
Senior testers who understand the application well enough to identify the right scenarios and risks for this specific release
Project managers in some organisations, particularly where testing is one component of a broader project management function
Because the test plan is a project-specific document, it is created at the start of each project or release cycle rather than maintained as a long-lived organisational document. The person who creates it should also own the responsibility for keeping it current as the project evolves.
Plan Purpose
The primary purpose of a test plan is to remove ambiguity from the testing process. When a test plan is well written, every person involved in the project knows what is being tested, who is responsible for each area, what the timeline looks like, and what done means.
Without a test plan, testing becomes reactive rather than structured:
Coverage gaps appear because nobody explicitly defined what needed to be tested
Deadlines slip because resource requirements were not planned in advance
Quality is inconsistent because different testers made different assumptions about scope
Stakeholders lose confidence because they have no visibility into testing progress or outcomes
A good test plan creates the conditions for testing to succeed by making every significant decision explicit before execution begins rather than discovering gaps under pressure during the testing cycle itself.
Types of Test Plans
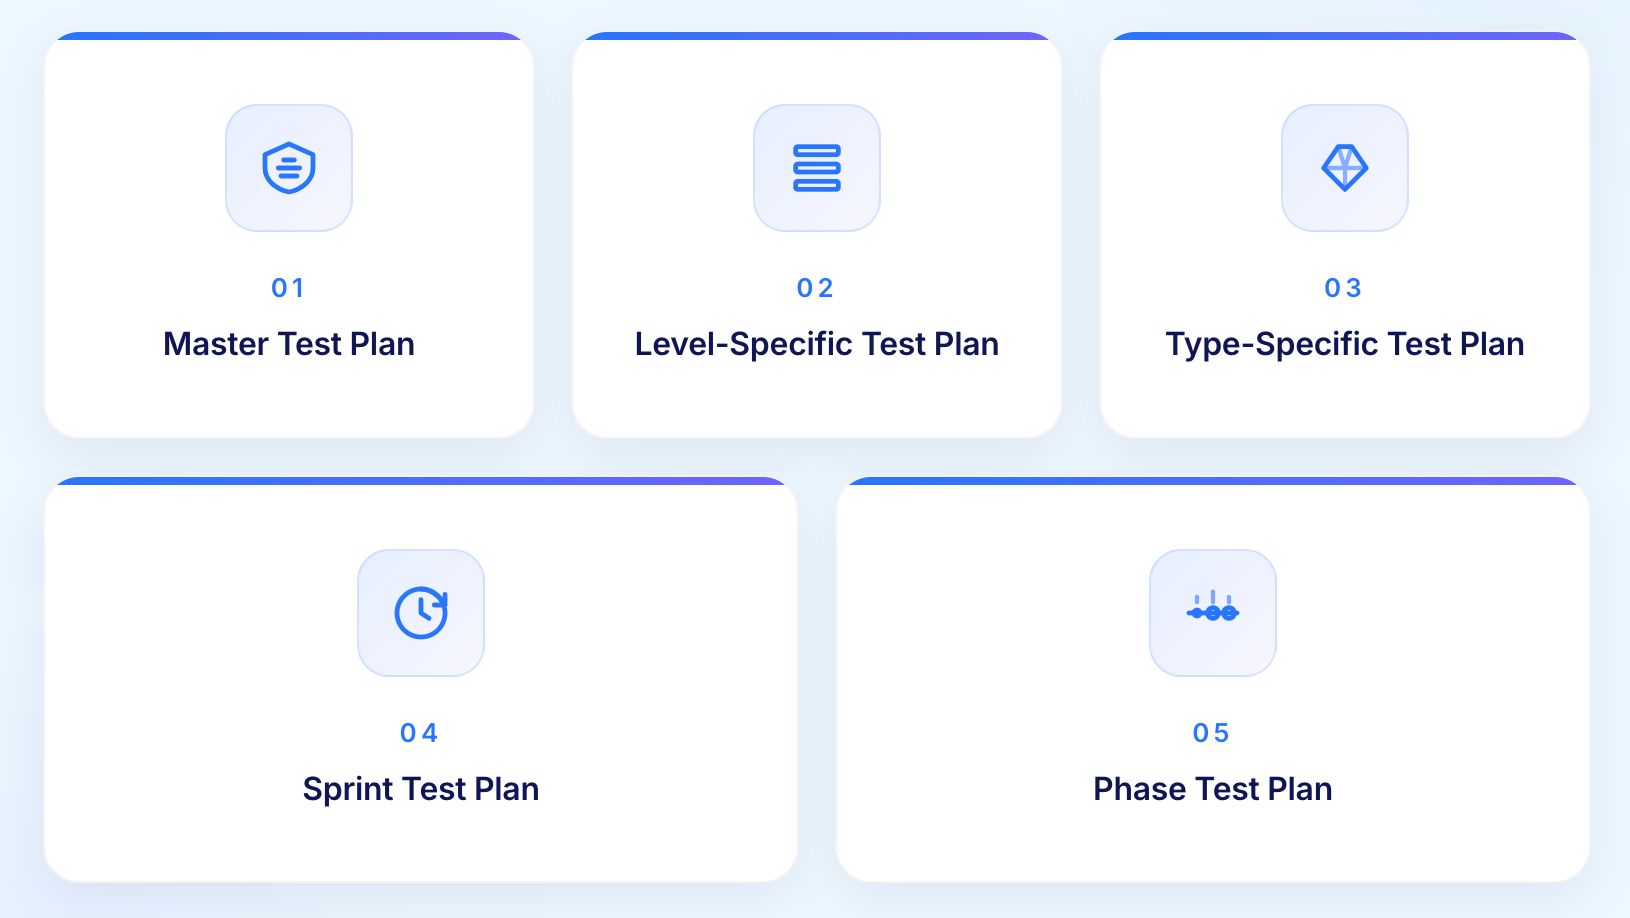
Test plans are not one-size-fits-all documents. The scope, depth, and format should match the context they are created for. Using a master test plan format for a two-week sprint creates unnecessary overhead. Using a lightweight sprint plan for a major system implementation leaves too many gaps.
1. Master Test Plan
High-level document covering the overall testing approach for an entire programme or system
Establishes the framework within which more detailed phase or component plans operate
Common in large enterprise implementations with multiple workstreams
2. Level-Specific Test Plan
Scoped to a specific testing level: unit, integration, system, or user acceptance testing
Each level has different objectives, environments, and participants
Prevents mixing concerns across testing levels
3. Type-Specific Test Plan
Scoped to a specific testing type: performance, security, accessibility, or usability
Documents the specialised approach, tools, environments, and success criteria for that quality dimension
4. Sprint Test Plan
Lightweight plan created at the beginning of each agile sprint
Covers user stories in scope, testing approach, resource assignments, and acceptance criteria
Intentionally brief and replaced at the start of each new sprint
5. Phase Test Plan
Covers a specific phase of a larger project such as system integration testing
Sits below the master test plan and above sprint or cycle plans
Provides the level of detail appropriate to a bounded phase
Key Differences: Test Strategy vs Test Plan
The distinction between a test strategy and a test plan is not just semantic. They serve fundamentally different purposes, are written for different audiences, and operate on different timescales. Understanding the differences prevents teams from creating documents that try to do both jobs and end up doing neither well.

Strategic vs Tactical:
Strategy: High-level approach and principles
Plan: Detailed execution specifics
Scope:
Strategy: Organization or program-wide
Plan: Project or release-specific
Timeframe:
Strategy: Long-term (12-24 months)
Plan: Short-term (2 weeks to 6 months)
Detail Level:
Strategy: Broad guidelines and frameworks
Plan: Specific scenarios and schedules
Change Frequency:
Strategy: Updated annually or with major shifts
Plan: Updated each project or sprint
Audience:
Strategy: Executive leadership and QA management
Plan: Testing teams and project stakeholders
How Test Strategy and Test Plan Work Together
The strategy and the plan are not competing documents. They serve different purposes and operate at different levels, but they are most effective when deliberately connected rather than created in isolation.
The Strategy Comes First
A test plan built without a strategy has no framework to align with. Each project team ends up making its own decisions about testing approaches, tools, and quality standards, resulting in inconsistency across projects and accumulated tool sprawl.
The strategy establishes the decisions that should not be remade for every project:
Which testing methodologies are standard
Which tools are approved
What quality gates are required before deployment
How risk is assessed and classified
The Plan Implements the Strategy
A strategy without a plan remains an aspiration. The plan translates strategic intent into the specific actions, timelines, responsibilities, and criteria that guide a real testing programme.
It answers the questions the strategy deliberately leaves open:
Which features are being tested in this release
Who is responsible for each area
What the schedule looks like
What constitutes acceptable quality for this particular deliverable
When They Need to Be Updated Together
Plans change frequently as project requirements evolve. Strategy changes infrequently, typically when the organisation adopts new tooling, shifts delivery methodology, or encounters regulatory changes. When the strategy does change, all active plans built from it need reviewing to ensure they remain aligned.
Equally, when a project plan repeatedly encounters situations the strategy did not anticipate, that is a signal the strategy needs updating rather than the plan working around a gap indefinitely.
Practical rules for keeping them aligned:
Every test plan should reference the test strategy it was built from
Any plan decision that contradicts the strategy should be explicitly flagged and approved rather than silently overridden
New team members should read the strategy before reading any project plan
Teams should not work around gaps in the strategy permanently
When to Create Test Strategy
Organizations benefit from formal test strategy documentation when:
Multiple Projects: Coordinating testing across many simultaneous projects requiring consistent approaches
Large Teams: Distributed QA teams needing unified testing philosophies and standards
Regulatory Requirements: Industries demanding documented quality management systems
Tool Standardization: Organizations selecting enterprise testing platforms requiring strategic justification
Quality Transformation: Shifting from manual to automated or waterfall to agile approaches
Not Always Required: Smaller organizations with single products and unified teams may operate effectively without formal strategy documents, relying on shared understanding.
How to Create a Test Strategy
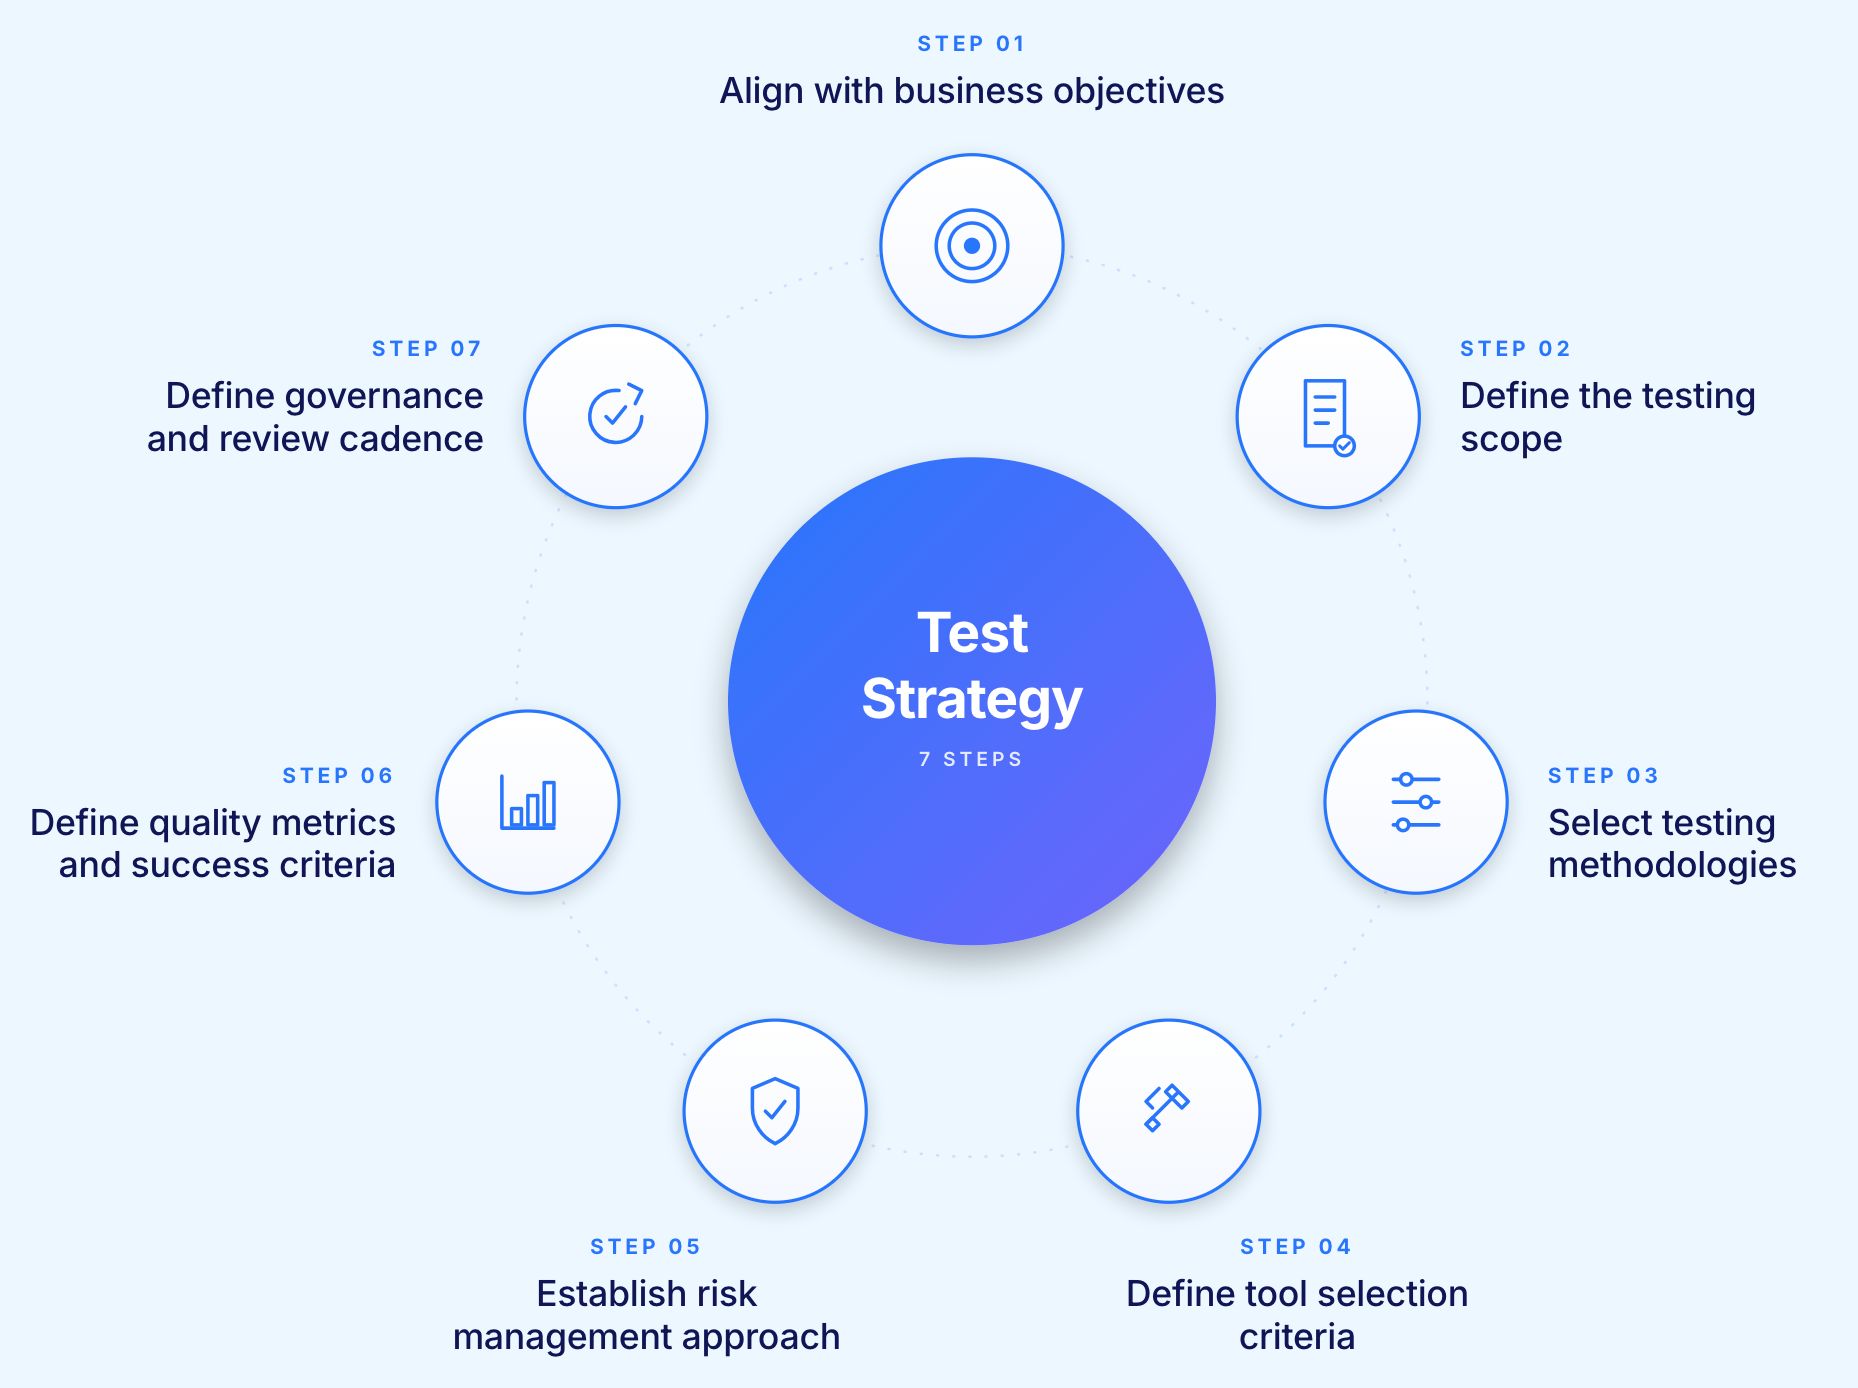
Step 1: Align With Business Objectives
Before defining any testing approach, understand what the organisation is trying to achieve. Faster time to market, regulatory compliance, customer retention, and cost reduction all imply different testing priorities. A test strategy that is not connected to business objectives is an internal QA document rather than an organisational quality framework.
Step 2: Define the Testing Scope
Establish which systems, applications, and integration points fall within scope. Be explicit about what is out of scope and why. Scope creep in test strategies creates documents that attempt to govern everything and end up governing nothing effectively.
Step 3: Select Testing Methodologies
Decide which testing approaches are standard for the organisation and document the rationale. Teams that understand why a methodology was chosen apply it more consistently than teams that follow it without understanding the reasoning behind it.
Step 4: Define Tool Selection Criteria
Rather than mandating specific tools, document the criteria that tool decisions should meet:
CI/CD integration capability
Support for the application types in the portfolio
Licensing model
Maintenance overhead
Criteria-based selection gives the strategy longevity because the criteria remain valid as tools evolve.
Step 5: Establish the Risk Management Approach
Define how risks are identified, assessed, and prioritised across projects. Establish a consistent risk classification framework so that a high-risk designation means the same thing on every project rather than being interpreted differently by each team.
Step 6: Define Quality Metrics and Success Criteria
Specify how testing effectiveness is measured. Useful metrics include defect escape rate, test coverage targets, regression pass rate, and mean time to detect. Measurable outcomes give the strategy something to evaluate against rather than remaining a set of aspirational statements.
Step 7: Define Governance and Review Cadence
Document who owns the strategy, how often it is reviewed, and what triggers an unscheduled review. A strategy that has no owner and no review schedule becomes outdated without anyone noticing.
When to Create Test Plans
Test plans prove valuable when:
Complex Projects: Large implementations requiring coordinated testing across teams
Stakeholder Alignment: Multiple stakeholders needing visibility into testing approach and coverage
Regulatory Compliance: Industries requiring documented testing evidence for audits
Resource Coordination: Multiple testers requiring clear assignments and schedules
Risk Management: High-risk projects benefiting from documented contingency plans
Agile Adaptation: Traditional comprehensive test plans give way to lightweight sprint test plans focusing on immediate deliverables.
How to Create a Test Plan
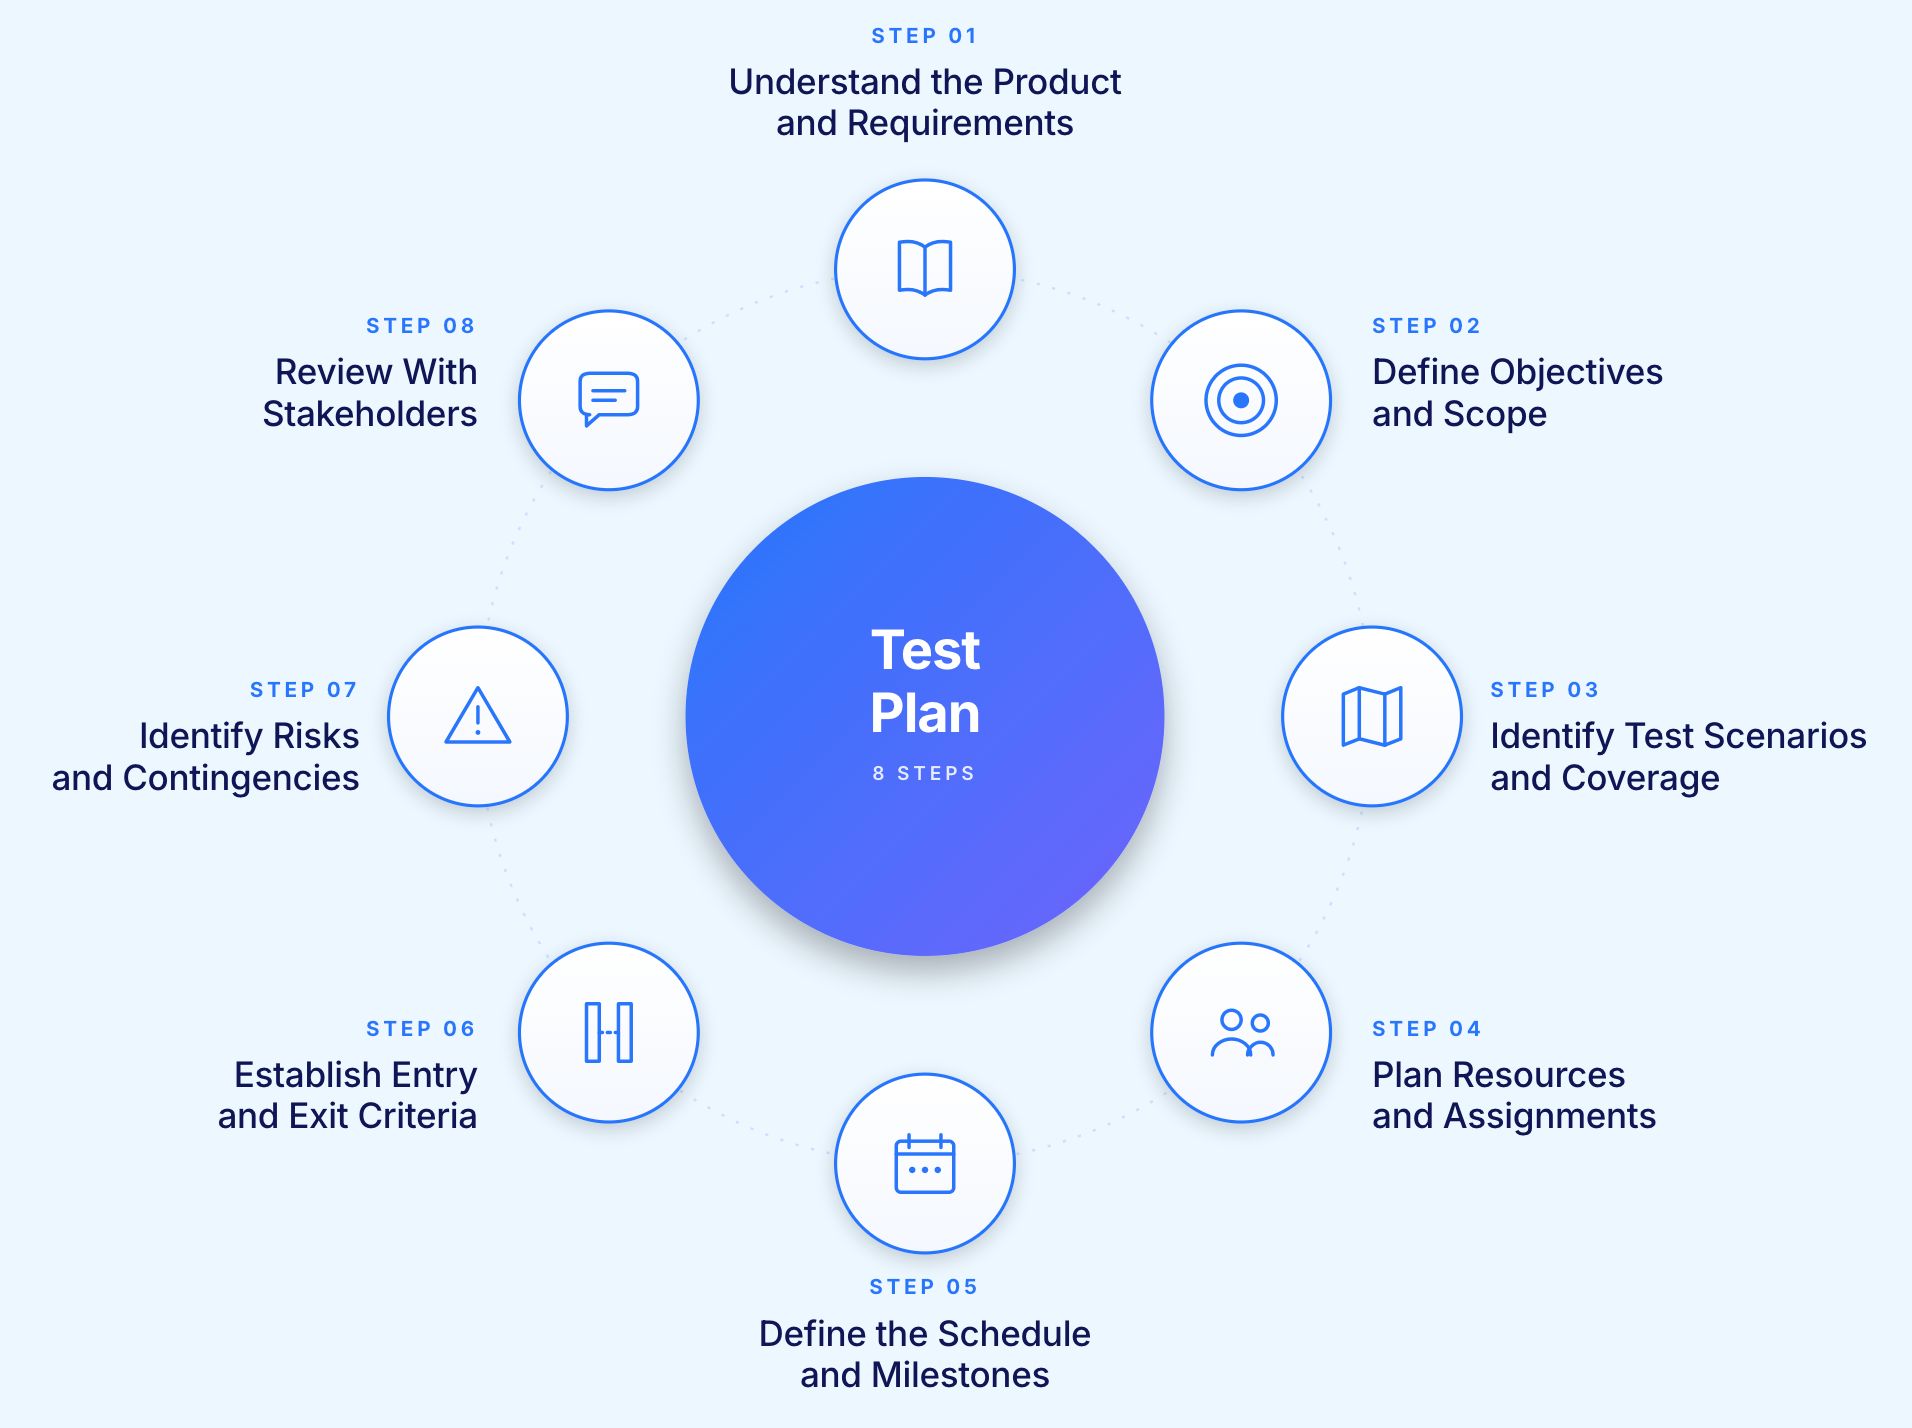
Step 1: Understand the Product and Requirements
Before writing a single test objective, spend time with the product, the requirements documentation, and the team members who understand the business context. Test plans written without this foundation tend to miss the scenarios that matter most.
Step 2: Define Objectives and Scope
Specify what the plan is designed to achieve and what falls within its scope. Be explicit about what is not being tested and why. Ambiguous scope is the most common cause of test plans that fail to provide the alignment they were created to establish.
Step 3: Identify Test Scenarios and Coverage Areas
Map the features and user journeys that need to be validated. Identify the risk areas that require deeper coverage and the lower-risk areas that can be covered more lightly. This mapping becomes the foundation for test case development.
Step 4: Plan Resources and Assignments
Identify who is responsible for each area of testing, what environments are required, what tools and access are needed, and what the dependencies are. Resource planning done after the schedule is set creates conflicts that could have been avoided.
Step 5: Define the Schedule and Milestones
Set realistic timelines for test case preparation, environment setup, execution, defect reporting, and sign-off. Build in time for defect resolution cycles. Plans that assume zero defects will be found during testing are not credible documents.
Step 6: Establish Entry and Exit Criteria
Entry criteria define the conditions that must be met before testing begins. Exit criteria define the conditions that must be met before testing is considered complete. Entry criteria prevent teams from testing against unstable builds. Exit criteria prevent teams from shipping without meeting the agreed quality standard.
Step 7: Identify Risks and Contingencies
Document the specific risks that could affect this project's testing programme and the contingency for each. Generic risk statements provide no actionable guidance. Specific risk statements with specific contingencies do.
Step 8: Review With Stakeholders Before Execution Begins
A test plan that has not been reviewed by the project team, product management, and relevant stakeholders before testing starts will encounter preventable surprises during execution. Review catches scope gaps, incorrect assumptions, and resource conflicts while there is still time to address them.
Test Strategy and Test Plan in Practice
Definitions and comparisons only go so far. Seeing how both documents apply to real scenarios makes the distinction concrete and shows how they complement rather than duplicate each other.
E-Commerce Platform: Pre-Peak Sale Testing
An e-commerce platform preparing for a major promotional sale has a clear risk profile. Payment processing, cart management, and checkout flows have the highest business impact if they fail.
The test strategy establishes:
Risk-based approach as the standard methodology
Customer-facing revenue flows receive the highest coverage priority in every release cycle
Performance testing is mandatory before any peak traffic period
Cross-browser regression is required for all checkout-related changes
The test plan for this specific release translates those principles into action:
Which tester owns checkout flow validation
Performance test scenario: simulating ten times normal concurrent user load
Browsers and devices in scope for cross-browser validation
Go/no-go criteria for each area
Escalation path if a critical defect is found before the sale goes live
The strategy answered what and why. The plan answered who, how, and when.
Financial Services Application: Regulatory Release
A financial services application releasing changes to its payment processing module operates in a heavily regulated environment. PCI DSS compliance, data encryption, and audit trail completeness are not optional quality attributes. They are legal requirements.
The test strategy establishes:
All releases touching payment processing must include security testing, encryption validation, and audit log verification
The compliance standards that apply to payment-related releases
Sign-off from the compliance team is a mandatory exit criterion
The test plan for this release specifies the practical execution:
Specific transaction scenarios to be tested
Encryption checks at each data boundary
Audit log entries that must be generated for each transaction type
Performance thresholds under expected concurrent load
Without the strategy, a plan might cover functional correctness but miss the compliance dimension entirely. The strategy ensures that dimension is always present regardless of who writes the plan.
SaaS Multi-Tenant Platform: Continuous Delivery
A SaaS platform deploying to production multiple times per week cannot rely on manual testing gates. The test strategy defines a continuous testing approach: automated regression runs on every commit, performance baselines are monitored continuously, and cross-tenant isolation is validated as part of every deployment pipeline.
The sprint test plan for a specific two-week cycle covers:
User stories in scope for that sprint
Automated scenarios being added for new functionality
Manual exploratory testing sessions planned for areas where automation coverage is thin
Acceptance criteria each story must meet before moving to production
The strategy makes continuous delivery safe by establishing the automation standard. The sprint plan makes it actionable by specifying what is happening in the next two weeks.
AI-Native Testing and the Role of Strategy and Planning
AI-native testing platforms change what test strategy and test planning look like in practice. They do not eliminate the need for strategic thinking. What they change is the execution overhead involved in implementing it.
What AI-native platforms reduce
Traditional testing programmes spent significant effort maintaining documentation that went out of date faster than it could be updated. AI-native platforms address three specific parts of that burden:
Self-healing tests keep automated coverage current without constant manual intervention
Natural language authoring lowers the barrier to creating coverage, reducing the resourcing overhead that detailed planning was designed to manage
Autonomous test generation handles some of the translation work between a test plan and actual execution automatically
What they do not replace
Strategic decisions still require human judgement. Choosing the right methodology, deciding which risk areas deserve the deepest coverage, and defining what acceptable quality looks like for a given release are decisions that require context and authority no platform can substitute for.
The strategy is still needed to answer why the organisation tests the way it does. The plan is still needed to answer what is being tested and who is responsible. Both documents can be lighter when the platform handles more of the execution complexity.
How Virtuoso QA fits in
Virtuoso QA is most effective within a testing programme that has strategic clarity. Teams that know their risk priorities and coverage targets can use Virtuoso QA to implement those decisions at scale through natural language authoring, self-healing automation, and AI Root Cause Analysis.
The practical outcome:
Test strategies focus more on principles and less on tooling specifics
Test plans can be lighter as autonomous generation reduces manual planning overhead
Time saved on maintenance redirects toward strategic thinking about what matters most to test and why
Related Reads:
Frequently Asked Questions
Do I need both test strategy and test plan?
Can test plans replace test strategy?
How often should test strategy update?
Do agile teams need test plans?
How does AI-native testing reduce documentation needs?
How do test strategies align with business objectives?